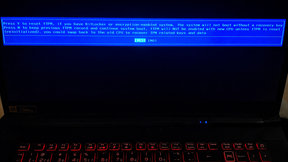
Remote resolution of an fTPM warning during laptop startup.
PC Služba s.r.o. (hereinafter referred to as the “Controller”) processes personal data in accordance with Regulation (EU) 2016/679 of the European Parliament and of the Council (GDPR), Act No. 18/2018 Coll. on Personal Data Protection and other applicable laws and regulations.
Company Name: PC Služba s.r.o.
Registered Office: Šustekova 16, 851 04 Bratislava - Petržalka, Slovakia
Company ID (IČO): 57 156 298
Email: pcsluzba@pcsluzba.sk
Phone: +421 911 758 922
PC Služba s.r.o. has not formally appointed a Data Protection Officer (DPO). The managing director is responsible for personal data protection, internal GDPR processes and handling security incidents.
Depending on the method of contact and the service provided, we may process in particular:
We process contact and service data for communication with customers, preparation and provision of the requested service, management of the service case and follow-up communication.
The legal basis is primarily taking steps at the request of the data subject prior to entering into a contract and performance of a contract pursuant to Article 6(1)(b) GDPR. Where processing of certain data is required by law, the legal basis is Article 6(1)(c) GDPR.
We process business contact details of persons acting on behalf of corporate customers for communication, organisation and provision of IT and service services. The legal basis is the Controller’s legitimate interest pursuant to Article 6(1)(f) GDPR in properly providing services and communicating with business partners.
In our internal PC Evidencia system, we process security and audit records which may contain user identification, the operation performed, time and IP address. The purpose is to protect the system and personal data, ensure traceability of changes and handle security incidents.
The legal basis is our legitimate interest pursuant to Article 6(1)(f) GDPR in securing information systems and protecting data.
We use Google Analytics 4 and StatCounter to measure website traffic. Analytics tools are activated only after consent to analytics cookies has been given through Silktide Consent Manager.
The legal basis for processing based on analytics cookies is your consent. You can change or withdraw your consent at any time through the cookie settings on the website. Further details are available on our Cookies page.
Data submitted through the contact form is sent to the email address pcsluzba@pcsluzba.sk. Data from the form is not stored separately in the website database.
We generally retain ordinary customer and service email communication for 5 years from the last relevant communication. If communication is required to handle a complaint, dispute or legal claim, it may be retained for as long as necessary to resolve the matter. Unsolicited, accidental and irrelevant messages are regularly deleted.
If you contact us via live chat, we process the text of your messages, replies from PC Služba, the conversation status and related timestamps so that we can handle your enquiry and continue the conversation. You can use live chat without creating an account and without providing an email address or telephone number.
After you send your first message, the chat may ask for your name or a nickname. You can provide it or skip this step. If you provide it, we use it to identify the conversation and communicate with you. It is retained as part of the conversation for the same period: no more than 90 days after the last activity.
After you send your first message, a record named pcslChatConversationV1, containing a conversation ID and a random technical token, is stored in your browser's local storage (localStorage). It allows you to return to the existing conversation. It does not contain message text, an email address or a telephone number. If you clear local storage, you will no longer be able to access the previous conversation without the original token. The server stores only a cryptographic hash of the token, not the original token.
To protect the service against misuse and excessive requests, we use time-limited technical records derived from the IP address using HMAC. These records are used to limit the number of requests (rate limiting).
We retain conversations and messages for no more than 90 days after the last activity, and technical rate-limiting records for approximately 2 days. When a new conversation is created, the system may send PC Služba an internal notification by email or SMS. The notification does not contain the text of your message or your contact details.
The legal basis for processing chat communications is taking steps at your request before entering into a contract or performing a contract pursuant to Article 6(1)(b) GDPR. Processing technical security data is based on our legitimate interest in protecting the service pursuant to Article 6(1)(f) GDPR.
We use the internal PC Evidencia application to organise service interventions. It may contain customer or contact person details, device information, service tickets, completed service work and technical notes.
We generally retain service history, tickets and related contact details for 5 years from the last service intervention or closure of the service case.
Technical documentation may be attached to a service record, for example a photograph of a device or screen, or another technical document needed to document a service intervention.
Passwords, login credentials, recovery codes, private keys or other customer authentication data must not be stored in service notes or attachments. Before an attachment is saved, it is checked for unnecessary personal data. Service attachments are generally retained for 3 years from closure of the relevant service case.
For remote support, we may use Remote Utilities Agent without permanent installation. The connection is established using an Internet-ID and password provided by the customer to the technician for the specific access. Once the intervention is completed, the Agent is closed and the remote connection ends.
Customer passwords used for remote access are not stored or recorded in PC Evidencia. According to the provider, data transmission within Remote Utilities is protected by end-to-end TLS encryption.
Retention periods depend on the type of data and the purpose of processing. In particular:
In Google Analytics 4, the retention period is set to 2 months for event data and 14 months for user data, with reset of the retention period on new user activity enabled.
When operating our services, external providers may be used to the extent necessary, in particular:
Data may also be disclosed to public authorities where we are legally required to do so.
We do not sell personal data or provide it to third parties for their own marketing purposes.
Some providers of technical or analytics services may process data outside the European Economic Area. Where use of a particular service involves such a transfer, it is carried out using mechanisms required by the GDPR for transfers of personal data to third countries, such as an adequacy decision or appropriate contractual safeguards in accordance with the relevant provider’s terms.
The production web space and databases are automatically backed up daily by Webhouse. The email service for the pcsluzba.sk domain is backed up at 14-day intervals. Retention of individual backup copies is governed by the current terms and configuration of the Webhouse service.
We use appropriate technical and organisational measures to protect data, including user access control, secure login, audit logs, protection of web communications via HTTPS and rules for data minimisation.
To the extent provided by the GDPR, you have in particular the right to:
You may exercise your rights at pcsluzba@pcsluzba.sk. Where necessary, we may reasonably verify the identity of the applicant in order to prevent disclosure of data to an unauthorised person.
If you believe that we process your personal data in violation of applicable law, you have the right to lodge a complaint with the Office for Personal Data Protection of the Slovak Republic.
We do not carry out automated individual decision-making or profiling in relation to personal data processing that would produce legal effects concerning you or similarly significantly affect you.
Questions regarding the processing of personal data and requests to exercise your GDPR rights may be sent to pcsluzba@pcsluzba.sk or you can contact us by telephone at +421 911 758 922.
Last updated: 30 September 2026
Remote resolution of an fTPM warning during laptop startup.
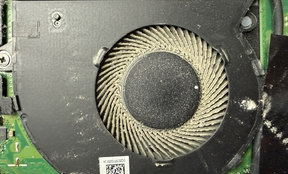
Dust cleaning from notebook.
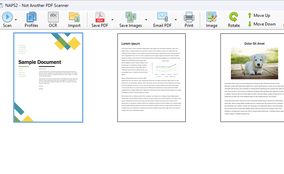
Installation of a document scanning application.
Windows 11 upgrade and setup.
We are available daily from 8:00 AM to 8:00 PM, including weekends at no additional charge.
Please call in advance to arrange an appointment.